Risk work with the evidence attached.
Regulatory filings, risk assessments and audit packages built from your documents, with every number traceable to its source. Less compiling, more reviewing.


 Backed by Y Combinator
From source documents to a defensible file.
Regulatory Reporting
Figures read from the statements, exposures aggregated and reconciled against last period's filing.
- In
- Financial statements, exposure data, prior filing.
- Extracted
- Figures read from the statements, exposures aggregated and reconciled against last period's filing.
- Out
- A report filled in, with an audit trail behind every number.
Risk Assessment
Key risk indicators and covenants read from the pack and compared to your thresholds.
- In
- Credit report, due diligence pack, financial statements.
- Extracted
- Key risk indicators and covenants read from the pack and compared to your thresholds.
- Out
- A scored assessment with the source of every metric.
Audit Q&A
The question is parsed, the control library, evidence store and policy archive searched, and the answer tied to the evidence.
- In
- A question in chat from the auditor or the control owner.
- Extracted
- The question is parsed, the control library, evidence store and policy archive searched, and the answer tied to the evidence.
- Out
- A cited answer in the chat, with the evidence linked for the audit file.
Runs where your documents already live.
- 01
On-prem or cloud
Runs inside your environment, on your hardware or your cloud account. Nothing leaves it.
- 02
One API, any model
Swaps between open-source and hosted models without touching the workflows built on top.
- 03
Your data stays yours
No training on your documents. Every value carries its source so reviewers can check it.
- 04
SSO, scoped by role
Plugs into your identity provider. Each workflow sets who can see, edit and approve.
- 05
Certified and audited
Publishes audited controls in a public trust center, so security review moves fast.
See it work.
All case studies →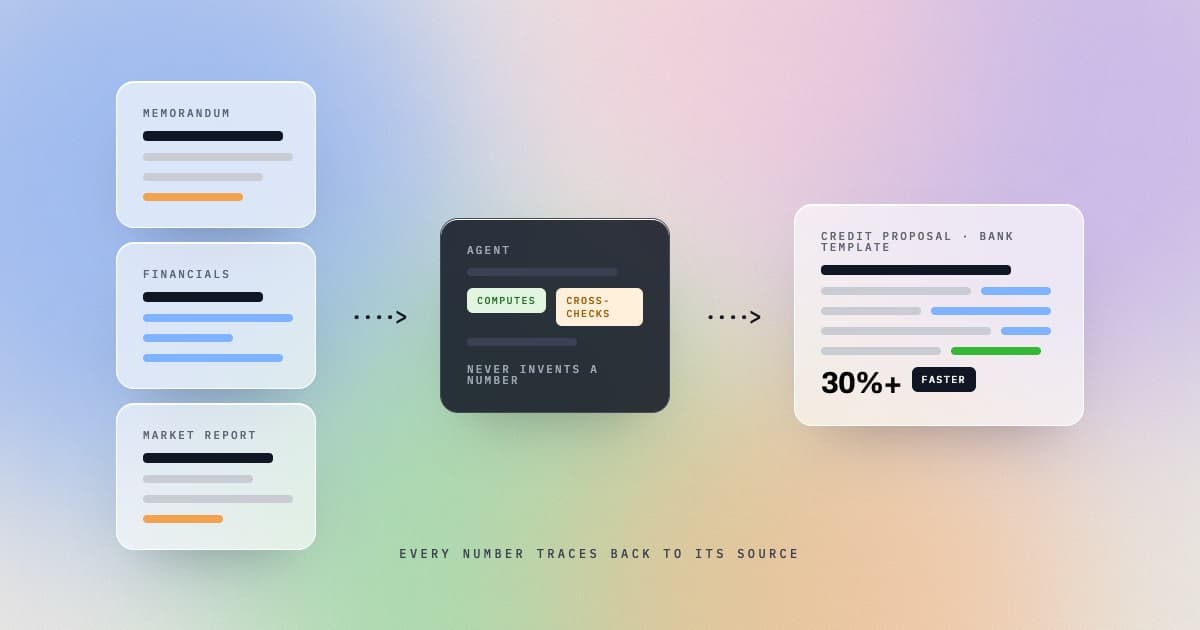
Drafting credit proposals for multi-million corporate loans
How a corporate bank cut credit proposal creation time by more than 30% with an agentic workflow that reads the deal pack, computes what is not stated and checks its own draft before an analyst sees it.
Read → · 2 min read
Turning a 50-document corporate loan folder into one cited summary
How a corporate bank cut relationship managers' meeting preparation time by 70% by classifying, consolidating and chat-enabling every client's loan documentation, with every answer cited to document, page and clause.
Read → · 3 min read